
Hotel, airport and café Wi-Fi can save mobile data, but check that the hotspot is genuine and that your device is not sharing more than you intend. HTTPS helps protect a connection to a website; it does not make a fake network or a scam page trustworthy.
Check the network name before you connect
Ask staff for the exact network name and login steps. A plausible label such as “Hotel Guest Wi-Fi” proves nothing on its own: someone setting up a fake hotspot can choose a name that looks almost identical to the official one.
Pay attention to the sign-in page that appears after you connect. A captive portal may ask for a room code or email address, but it should not prompt you for your bank password or email password. If the request does not match what staff described, stop and check with them.
The network and the website are separate checks. Knowing that an airport runs the hotspot does not prove that every page you open is legitimate. Check the domain, be wary of urgent requests, and do not approve sign-in prompts you did not initiate.
Open Wi-Fi, WPA2/WPA3 and HTTPS protect different things
An “open” network usually lets you connect without a Wi-Fi password. Depending on how it is configured, radio traffic between your device and the access point may not have the protection offered by an encrypted Wi-Fi network. Implementations vary, so the network name alone cannot tell you exactly what protection is in place.
WPA2 and WPA3 protect the wireless link between a device and an access point according to the network’s configuration. A password shared with many guests does not mean you should trust every connected device or the hotspot operator. Client isolation also depends on the venue’s equipment and settings.
HTTPS protects data exchanged between your browser and the website named in the address. The Federal Trade Commission notes that widespread website encryption means public Wi-Fi is usually safe to use, but a scammer’s website can also use HTTPS. The browser’s lock icon shows that the connection to that domain is encrypted; it does not prove that the domain is the one you meant to visit or that the site is honest.
What a VPN adds — and what it cannot do
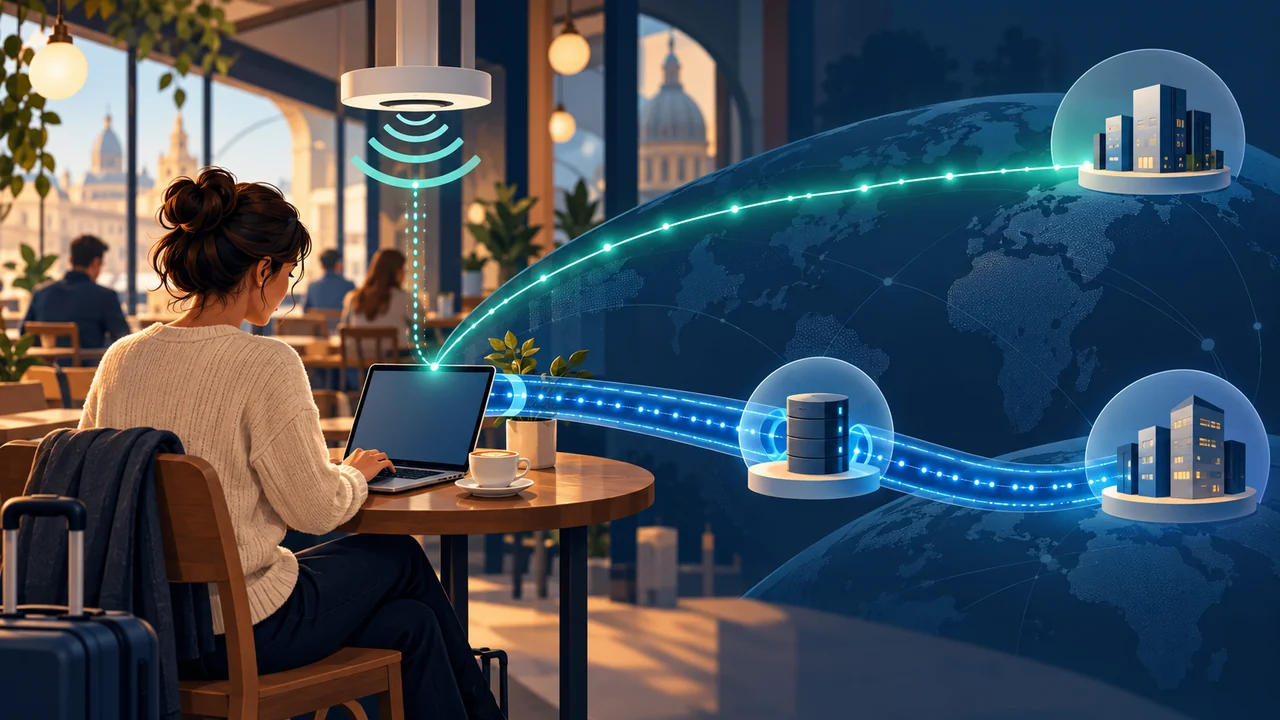
A VPN creates an encrypted tunnel between your device and a VPN server. It can make traffic routed through that tunnel harder to read on the local network, but the tunnel ends at the VPN server. It cannot secure a compromised device, detect every phishing attempt, or make a fake page or malicious app safe.
Not all traffic necessarily goes through the VPN: split tunnelling or excluded apps can leave some connections outside the tunnel. The VPN provider also becomes an important intermediary, so choose it carefully. The UK National Cyber Security Centre says only traffic routed through the VPN is protected. For work, follow your organisation’s instructions: a company VPN may have different requirements and settings from a personal service.
A VPN can be useful in a specific situation, but it is neither an absolute security guarantee nor a requirement for every hotspot.
Limit what nearby devices can see
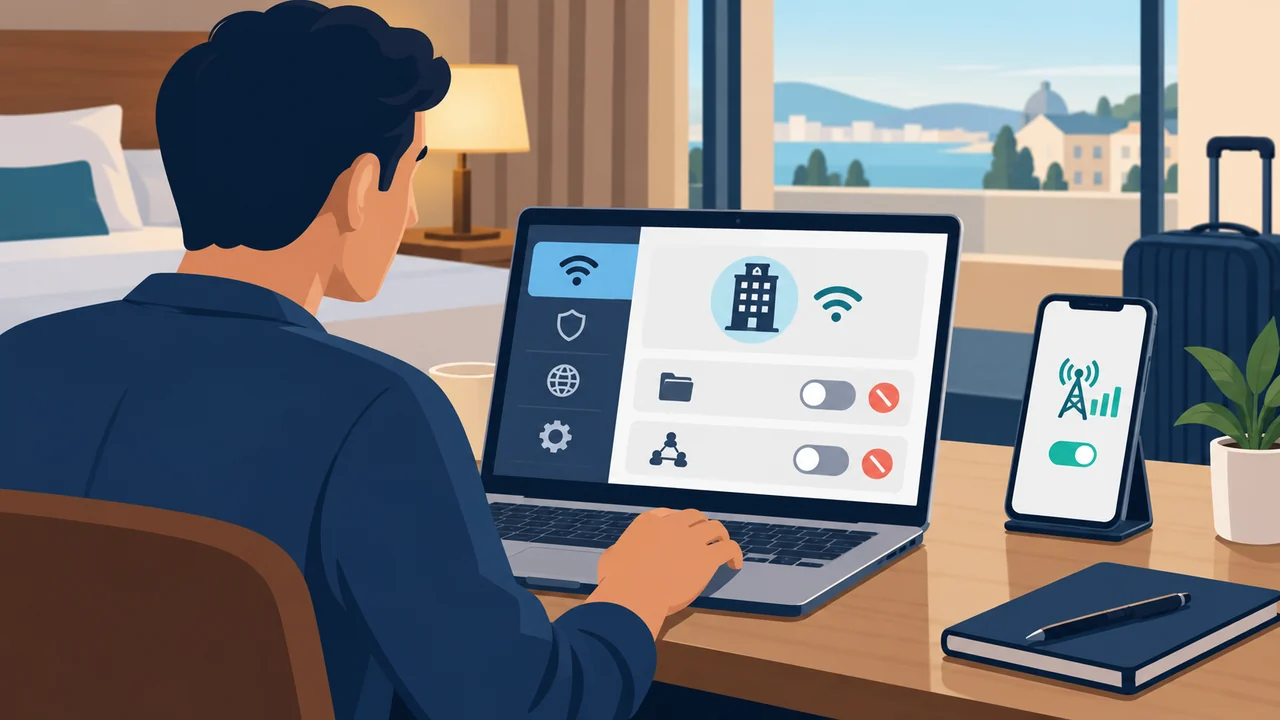
On Windows, check the network profile and choose “Public” when connected in a public place. Microsoft explains that a private profile makes the PC discoverable and allows file and printer sharing. On a Mac, turn off File Sharing in System Settings > General > Sharing when you do not need it.
Turn off automatic connection to hotspots you no longer use and remove saved networks you do not trust. Limit nearby sharing too: Apple lets you choose “Contacts Only” or turn AirDrop off until you need to send something. Menu names and options vary on Android and Windows; look for nearby-sharing settings and make the device visible only when needed.
Keep your operating system and apps up to date. Updates do not make a venue’s Wi-Fi trustworthy, but they reduce exposure to problems the manufacturer has already fixed.
When mobile data is the better choice
For sensitive tasks, or when the Wi-Fi name or sign-in page seems suspicious, cellular data or your personal hotspot is often the more cautious option. If a hotspot seems suspicious, mobile data keeps you off the venue’s local network; check coverage, roaming and plan costs all the same.
Check coverage, data allowance and cost too. Roaming conditions change by destination, while a travel eSIM depends on device compatibility, partner networks and location. See our guides to travel eSIMs and EU roaming.
A quick checklist before browsing
- Confirm the SSID and sign-in steps with staff; do not trust a network just because its name looks familiar.
- Check website addresses and use HTTPS, remembering that encryption does not verify that a page is legitimate.
- Set the network as public and turn off sharing and visibility you do not need.
- Use mobile data for sensitive activity if the hotspot does not feel right and your plan allows it.
- Use a VPN only when you understand who operates it and what it protects; it is not a fix for every risk.
Comments
Comments
Join the discussion respectfully: reasoned criticism is welcome; avoid threats, abuse, personal data and promotional links.
To join the discussion, you'll need to sign in with your WordPress.com account. This feature will be available when the site launches.